Campus ID News
Card, mobile credential, payment and security
FEATURED
PARTNERS

Campus security - time for a change?

CampusIDNews Staff   ||   Jan 19, 2010  ||   

Security challenges faced in enterprise-wide computer networks are likely to become a hallmark of 2010.

Organizations are moving to a Secure Network Fabric to respond and address the constant need for security and policy enforcement throughout the network, says Derek Wiggill, 3Com Africa regional sales director. “A network security solution needs to ensure that only legitimate network packets reach their appropriate destinations”.

A Secure Network Fabric is described as having real-time automated remediation, where threats are blocked and/or corrected in real-time within the network, identifying illegitimate packets and dropping them. Global enforcement should also be imposed everywhere in the network topology, rather than using chokepoints. Enforcement management must also be centralized, reducing inconsistencies and costs.

University and large campus networks are focusing on identity-based policies and user access management issues because they experience a large population of users, bringing their own unmanaged systems on to the internal network, and are not completely trusted. Assigning new users to groups, such as staff and administrators, or grouping students by major, can ensure appropriate access to various resources in a manageable fashion.

To read more click here.
Subscribe to our weekly newsletter

RECENT ARTICLES

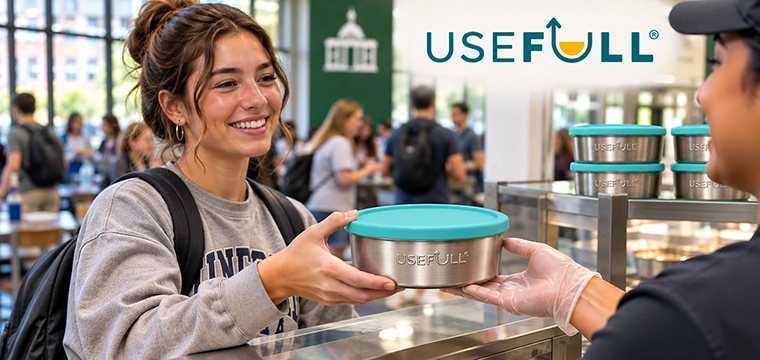
College student getting a stainless steel reusable container from USEFULL for a take out meal at a campus dining location
Nov 12, 26 /

USEFULL's stainless steel containers remove plastic from reusable dining programs

As colleges and universities look for ways to reduce disposable packaging in campus dining, reusable container programs have become an increasingly popular option. But while many solutions rely on reusable plastic containers, USEFULL is taking a different approach. It provides stainless steel containers supported by technology that tracks checkout, returns, and inventory. For Alison Cove, […]
Student use id card in cafeteria at University of Oregon

University of Oregon selects FutureState for campus credential management

FutureState announced that the University of Oregon has selected its platform to modernize credential management across campus. FutureState provides a credential management platform and an integration management solution that enables flexible connections between access control, transaction, dining, and many more essential campus systems. Under the agreement, the university will deploy CardSync for credential lifecycle management, […]
CampusIDNews: Open standards for campus mobile credentials series intro graphic for part 2 on PKOC

Part 2: Exploring the PKOC standard for campus mobile credentials

Campus access control systems are built to answer the seemingly straightforward question, “Should this person be allowed through this door?” But before the system can make that decision, it first must answer the question, “Is the credential itself legitimate?” That is the precise question the Public Key Open Credential standard was designed to answer, and […]
CIDN logo reversed
The only publication dedicated to the use of campus cards, mobile credentials, identity and security technology in the education market. CampusIDNews – formerly CR80News – has served more than 6,500 subscribers for more than two decades.
Twitter

Great inverview on the Public Key Open Credential (PKOC) standard with ELATEC's Jason Ouellette, Chairman of the Board for the @PSIAlliance.

Attn: friends in the biometrics space. Nominations close Friday for the annual Women in Biometrics Awards. Take five minutes to recognize a colleague or even yourself. http://WomenInBiometrics.com

Load More...
Contact
CampusIDNews is published by AVISIAN Publishing
315 E. Georgia St.
Tallahassee, FL 32301
www.AVISIAN.com[email protected]
Use our contact form to submit tips, corrections, or questions to our team.
©2026 CampusIDNews. All rights reserved.