Campus ID News
Card, mobile credential, payment and security
FEATURED
PARTNERS
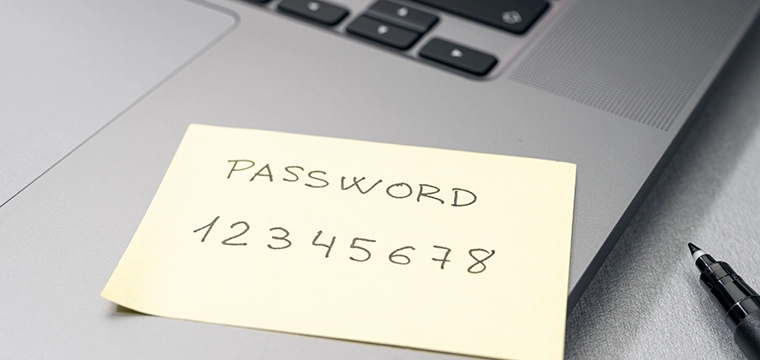
Password written on sticky note

New study shows password crisis worsening as weak and reused credentials remain dominant

Just 6% of all passwords considered secure against common attack vectors

CampusIDNews Staff   ||   May 09, 2025  ||   

A new study by the Cybernews research team examined a dataset containing more than 19 billion passwords made public in recent breaches. The goal was to determine the number of weak vs. strong and unique vs. reused passwords.

The results were far from encouraging.

Researchers looked at exposed credentials from about 200 breaches that occured between April 2024 and April 2025.

Passwords containing ultra-common terms like “password”, “admin”, and “123456” remain the most common.

One researcher called it an epidemic of weak password reuse, with just 6% of passwords being unique. For the other 94% of weak or reused passwords, the only defense against dictionary attacks is two-factor authentication.

Despite a decade-long effort to educate users about password security, there has been little progress.

Common terms, short passwords prevalent

Users included “1234” in 4% of all passwords. “Password” and “123456” have been the most common passwords throughout the 2010s and 2020s.

People's names were the second most prevalent component. The 100 most popular names of 2025 were included in 8% of all passwords. Common words like “love” and pop culture terms like “batman” were also extremely reused.

42% of all passwords are between 8 and 10 characters, but experts say 12-characters is the minimum to ensure security.

Most people use eight-to-ten-character passwords (42%), with eight the most popular.

One-third (27%) contain only lowercase letters and digits, significantly increasing vulnerability.

But this is changing.

Research from 2022 found that only 1% of passwords used a mix of lowercase, uppercase, numbers, and symbols. This 2025 study found that number has grown dramatically to 19%, likely due to stricter platform requirements.

Protecting your accounts

In addition to researchers, attackers have access to these password lists and many others. As new breaches occur, they add to their lists and continually refine attacks.

Weak, reused, and obvious passwords increase your chance to fall victim to an attack. If you reuse passwords across multiple services and accounts, a breach in one system can compromise other accounts.

More than one-quarter of the passwords contain only lowercase letters and digits, rather than the recommended mix of uppercase, lowercase, digits, and special characters.

All users should take steps to improve their password habits.
  • Use a password manager
  • Never reuse passwords and make sure they include a mix of at least 12 characters of all character types.
  • Use multi-factor authentication (MFA)
  • Set up password policies within your organization to meet these requirements.
Subscribe to our weekly newsletter

RECENT ARTICLES

Student use id card in cafeteria at University of Oregon

University of Oregon selects FutureState for campus credential management

FutureState announced that the University of Oregon has selected its platform to modernize credential management across campus. FutureState provides a credential management platform and an integration management solution that enables flexible connections between access control, transaction, dining, and many more essential campus systems. Under the agreement, the university will deploy CardSync for credential lifecycle management, […]
CampusIDNews: Open standards for campus mobile credentials series intro graphic for part 2 on PKOC

Part 2: Exploring the PKOC standard for campus mobile credentials

Campus access control systems are built to answer the seemingly straightforward question, “Should this person be allowed through this door?” But before the system can make that decision, it first must answer the question, “Is the credential itself legitimate?” That is the precise question the Public Key Open Credential standard was designed to answer, and […]
Ed Sullivan from EntryReady gives a video interview on EntryReady's expansion into higher ed with Apple, Google and Samsung wallet support

EntryReady expands into higher ed with Apple, Google, Samsung wallet support

Ed Sullivan, Chief Strategy Officer and co-founder of EntryReady, discusses how the company's experience in hotel access control is shaping its expansion into higher education. After developing NFC- and RFID-based locking systems for hotels and resorts, EntryReady is looking to bring that technology to campus residence halls, replacing traditional brass keys with mobile wallet credentials. […]
CIDN logo reversed
The only publication dedicated to the use of campus cards, mobile credentials, identity and security technology in the education market. CampusIDNews – formerly CR80News – has served more than 6,500 subscribers for more than two decades.
Twitter

Great inverview on the Public Key Open Credential (PKOC) standard with ELATEC's Jason Ouellette, Chairman of the Board for the @PSIAlliance.

Attn: friends in the biometrics space. Nominations close Friday for the annual Women in Biometrics Awards. Take five minutes to recognize a colleague or even yourself. http://WomenInBiometrics.com

Load More...
Contact
CampusIDNews is published by AVISIAN Publishing
315 E. Georgia St.
Tallahassee, FL 32301
www.AVISIAN.com[email protected]
Use our contact form to submit tips, corrections, or questions to our team.
©2026 CampusIDNews. All rights reserved.